
 +44 20 3695 6722
 Sign in
On-Premises DDoS Protection
StormWall Appliance
The top-tier StormWall cloud protection — now inside your perimeter

13 years of Cloud DDoS Protection, Now On-Prem
Battle-tested against real DDoS attacks for over a decade. Now packaged for your on-prem deployment.

Bring Your
Own Hardware
Deploy on servers you already have. Replace hardware without re-licensing. No proprietary appliance to buy or maintain.

One License —
Everything Included
L3–L5 OSI protection, specialized filters, clustering, dashboards, API — all in one license, no add-ons required.
What Is StormWall Appliance
StormWall Appliance is on-premises DDoS protection software for your network infrastructure.
It runs on your hardware and processes traffic locally, so nothing ever leaves your perimeter.
Under the hood is StormWall's proprietary technology: DPDK-based low-level packet processing and high-speed filtering algorithms.
It handles massive traffic volumes with minimal latency, even during large-scale DDoS attacks.
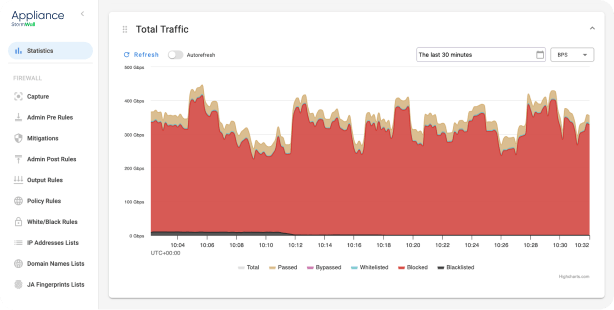
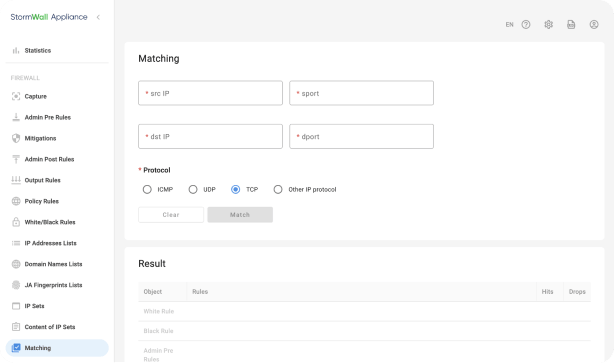
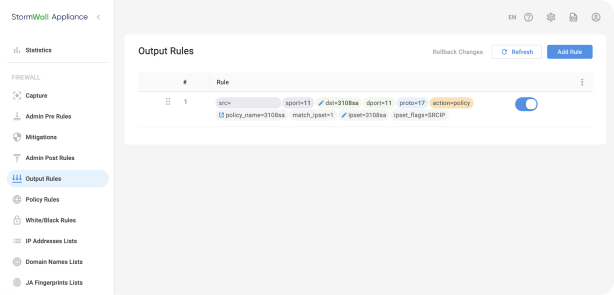
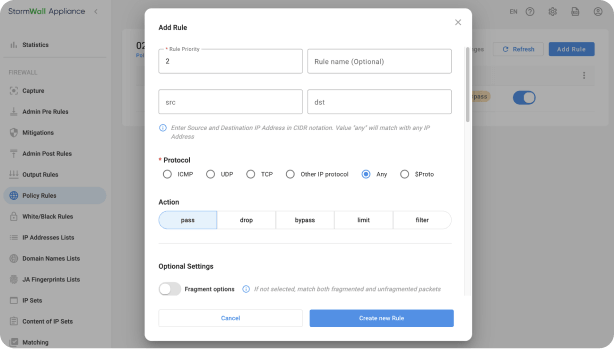
Available from a Single License
All protection features, filters
and tools — in one license

L3–L5 OSI DDoS Protection
Enterprise Service Protection (VPN, SIP, etc.)
Protocol-Aware Filters for DNS, QUIC, and TLS JA3
Traffic Capture
and Analysis (PCAP)
Customizable Dashboards and Metrics
Operation in Isolated Networks
Filtering Node
Basic Support Included in Year 1
REST API for
External
Integrations
Gaming Protocol Protection (RakNet,
SA-MP, CS, Steam)
How It Works
Per-packet real-time DDoS filtering

Legitimate Users
Regular Traffic

DDoS Attack
Malicious Traffic

StormWall Appliance
Multi-Layer DDoS Filtering
at L3–L5 OSI

Your Infrastructure

Filtered-Out DDoS Attack
What You Get
Additional benefits of StormWall Appliance

Simple, Fast Integration
Fits into your existing network architecture with no significant changes required.

Flexible Licensing
Billed by active port capacity. Perpetual license or annual Subscription — no hidden fees.

Clustering and Scaling
Protects infrastructure at any scale — from individual services to large carrier networks.

In-House Developed
Full control over roadmap, updates and support — no third-party dependencies.
Book a Demo
Attacks It Protects Against
The solution covers all modern
DDoS attack vectors, including:
Licensing Models
Choose the model that fits your budget
Subscription
Annual subscription
- Use for the subscription term
- Basic support included for year 1
- Optimal for project-based work (OpEx); lower upfront cost
Perpetual
One-time purchase
- Unlimited term
- Basic support included for year 1
- Optimal for long-term use (CapEx)

Starting configuration: 10 Gbps. On 2- and 4-socket servers, we deploy 2 or 4 software instances with capacity split equally between them. Final pricing is based on active port capacity, number of installations and support tier.
Support Tiers
From basic maintenance to fully
outsourced protection
Basic
17% of annual cost
- Ticket-based support, no guaranteed SLA
- Regular patches and updates
- Documentation and knowledge base
- Client handles attack response and rule configuration independently
For teams with information-security expertise
Recommended
Advanced
30% of annual cost (+13% in year 1)
- 24/7 ticket intake with guaranteed SLA
- Out-of-cycle patches for non-critical bugs
- Active implementation support
- Response time: from 1 hour
For mid-sized teams and growing clients
Private
Custom, on request
-
 StormWall SOC takes over protection 24/7
-
Dedicated technical account manager
-
Rule configuration and attack mitigation handled by our team
-
Regular incident reports
-
Response time: 15 minutes
Fully outsourced protection —
for teams without in-house DDoS expertise
Downloadable Materials
Everything you need to get started
with the product
How to Get Started
We support you at every step —
from request to full implementation
01
Qualification
Submit a request, complete the intake form, or ask sales
for a demo
02
Compatibility Check
Send us your server configuration — we’ll verify compatibility
03
License Issuance
License tailored to your active port capacity, support tier,
and number of deployments
04
Deployment
Install from our private repository. Up and running in as little as one day
05
Free 30-Day Trial
Test it on your traffic at no cost. Switch to a paid plan when you're ready
Why StormWall Appliance
Architecture and deployment consultation
Product demo based on real-world scenarios
Pilot testing in your own infrastructure
Right-sized configuration and licensing model
Rapid quote turnaround
On-site support
Book a Demo
Frequently Asked Questions
How does StormWall Appliance differ from StormWall’s cloud protection?
Both share the same StormWall filtering technology, delivered in two formats. In the cloud, traffic first passes through our filtering network and reaches you already cleaned. With Appliance, the solution is deployed inside your own infrastructure: traffic is processed on your servers and data does not leave your perimeter.
The cloud is quicker and easier to enable, while Appliance gives you full control over your traffic and data. The attack profile also matters: steady attacks within your channel capacity are effectively filtered by Appliance, while high-volume peak attacks that exceed the channel’s bandwidth are handled by our cloud protection.
Which fits your case depends on your security team requirements, industry regulator and attack profile — we’ll help you decide during the first project discussion.
Does StormWall Appliance work on its own, or together with the cloud?
Both modes are supported — your choice.
Standalone.
Appliance is deployed within your perimeter as a full-fledged on-premises DDoS protection at L3–L5 OSI: volumetric floods, TCP stack attacks, DNS, gaming protocols and attacks in encrypted traffic.
In tandem with StormWall cloud protection.
Adds application-layer (L7) protection — HTTP Flood, Slow HTTP, WAF. For high-volume attacks exceeding your channel bandwidth, StormWall cloud protection may be used. The specific integration scenario is discussed on a case-by-case basis.
Do we need to buy hardware from you?
No. StormWall Appliance is delivered as software and runs on your servers — physical or virtual. Standard x86 platforms that meet the system requirements are sufficient.
We recommend using hardware platforms that have passed StormWall internal testing. Deployment on other platforms is allowed — in that case compatibility is assessed individually. The license is bound to active port capacity, not to specific hardware — you can replace a server without re-issuing the license.
We don’t have a dedicated DDoS team. Who will tune rules and mitigate attacks?
It depends on the support tier. On Basic you manage the solution yourself; we provide updates, documentation and ticket responses — suitable for teams with in-house InfoSec expertise.
On Advanced you get guaranteed SLA by incident priorities and active hands-on assistance from our engineers during deployment.
If you have no in-house team at all, there is the Private tier: StormWall specialists take over the solution completely — our engineers configure rules, mitigate attacks, investigate incidents and send reports, and you get a dedicated technical account manager. In effect, you get an on-premises solution managed like a cloud service — a rare offering in the on-premises market.
Is the solution suitable for the public sector, critical infrastructure operators and isolated networks?
Yes. Traffic is processed locally and never leaves your perimeter. For isolated networks without internet access, an offline licensing option with a hardware key is available — the solution operates without connecting to StormWall servers.
On-site deployment support (available on request).
Can we test the solution before purchasing?
Yes. After deployment, a free trial begins — running on real traffic, in your own infrastructure and, if needed, alongside the solution you currently use. The deployment itself takes as little as one day — including setup and starting filtering.
The demo has no strings attached: if the result doesn’t suit you, you simply don’t move on to commercial operation.
