Under Attack?
Поиск

StormWall for Web

WAF

+

DDoS Protection

+

Antibot

Unified solution for protecting websites, web apps, APIs, and HTTP
services. Built to keep your resources secure, resilient, and always online.

Globee Awards 2025 Gold Winner. Cybersecurity
Globee Awards 2023 Gold Winner. Cybersecurity
10 min

Deployment

> 8 000 Gbps

Filtering capacity

> 1 500 clients

Protected worldwide

15 min

Response time

Built for what modern
attacks really look like

Same protection quality
at every pricing plan

The only difference is functionality and level of support.

8+ Tbps capacity,
9 PoPs worldwide

Built to filter attacks of any scale
close to their origin.

Instant
chat support

15-minute response from our team.
Available on Business and Enterprise.

Léo Delsart

Léo Delsart

CTO

I2SNETWORK, Hosting Provider

Partnering with StormWall has been one of the biggest highlights of 2024. We’ve gained not only a reliable business partner but also a powerful DDoS protection solution with fast support and low latency.

One bundle — Zero threats

No need to buy separate solutions.
Get StormWall for Web and focus on what matters most.

built-in

managed

Essential WAF

Cuts junk traffic by geo, IP and rate

  • GeoIP & geo-blocking
  • Header & path filtering
  • Rate limiting
  • IP Black / White lists

L3

L4

L5

L7

scalable

instant

DDoS Protection

Keeps your site online during attacks

  • Up to 8 Tbps global filtering capacity
  • Sub-second detection and mitigation
  • SSL-free filtering (PCI DSS compatible)
  • Unlimited attack volume, duration, count
  • Deploy during an active attack in 10 min

JA3

JA4

AI/ML

invisible

Antibot

Stops malicious bots. Lets real users in

  • ML-powered detection
  • Blocks scrapers, credential stuffing & account abuse
  • Fingerprints bots by JA3/JA4
  • Lets Googlebot, Bingbot & monitors through
  • Skips CAPTCHAs, friction, and false blocks

Advanced WAF

The bundle above stops floods, bots and junk traffic.
Advanced WAF stops attacks on the application itself.

Purchased separately

Advanced WAF Business

Signature-based application security

  • OWASP Top 10 (SQLi, XSS, RCE)
  • HTTP protocol validation
  • Automatic static-resource filtering
  • Application-wide rate limiting
  • Anomaly-based blocking (LRU)

Purchased separately

Advanced WAF Enterprise

Adaptive application security

Advanced WAF +

  • Application business-logic model (ML)
  • User & session control
  • Per-action rate limiting
  • API validation against OpenAPI schemas
  • SIEM integration
  • Warm-data storage + retrospective analysis
  • WAF API and raw-query access
  • Dedicated installation

Billed for clean traffic.
Not for attacks

Plans scale features and response time.
The engine — same. The SOC — same. Protection quality — same.

Currency:
USD
USD
EUR
Compare plans

Personal

Real protection for personal
sites and side projects.

  • 1 domain
  • 25 Mbit/s bandwidth
  • < 3‑hour first response
  • 98% uptime SLA
  • Essential Antibot
  • IP white/black lists (100)
  • Notifications
  • Load balancing
  • SSL‑free filtering
  • Graylog
  • Chat support

Most Popular

Business

Configurable protection
for growing companies.

  • 1 or more domains
  • 50+ Mbit/s bandwidth
  • < 30‑min first response
  • 99.2% uptime SLA
  • Essential Antibot
  • IP white/black lists (1 000)
  • Notifications
  • Load balancing
  • SSL‑free filtering
  • Graylog
  • Chat support

Enterprise

Premium protection
with our fastest reaction times.

  • 1 or more domains
  • 50+ Mbit/s bandwidth
  • < 15‑min first response
  • 99.5% uptime SLA
  • Advanced Antibot
  • IP white/black lists (5 000)
  • Notifications
  • Load balancing
  • SSL‑free filtering
  • Graylog
  • Chat support
  • Dedicated IP

Different pricing plans. Same protection quality.

Philipp Moser

Philipp Moser

CEO

Limitis, IT Service Provider

StormWall protects our servers from attacks before our customers even notice. This level of security is worth its weight in gold — both technically and from a business perspective. The speed and precision of their response is impressive.

The dashboard you'll
actually want to open

Every setting, every log, every rule — on all pricing plans. Nothing gated.
Nothing hidden behind "contact sales."

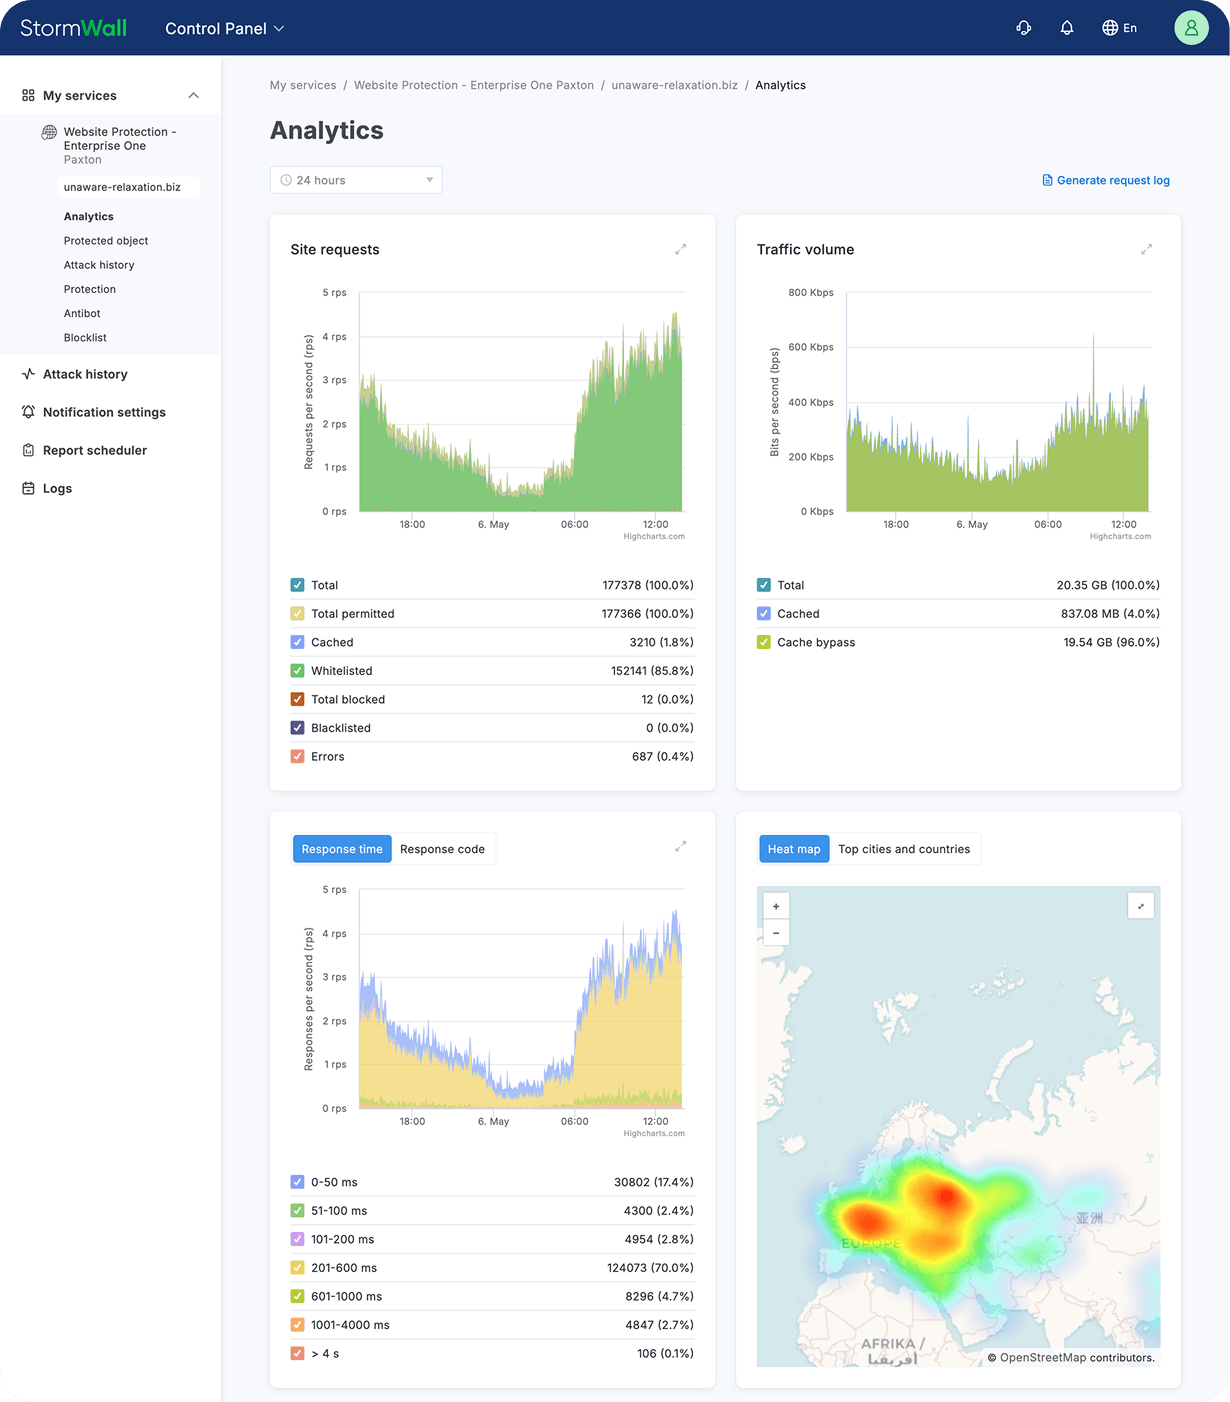
Analytics — Client Portal
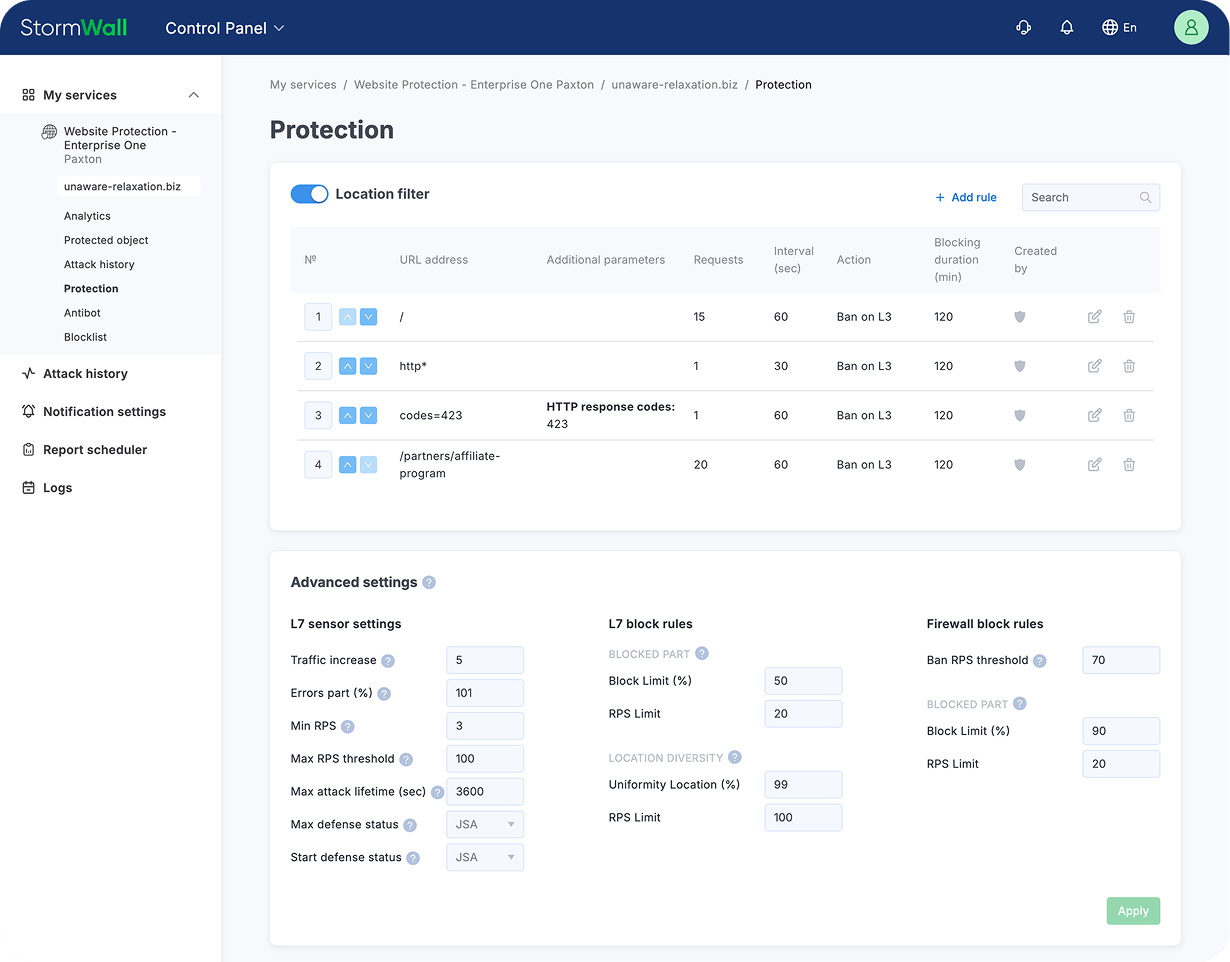
Protection settings — Client Portal
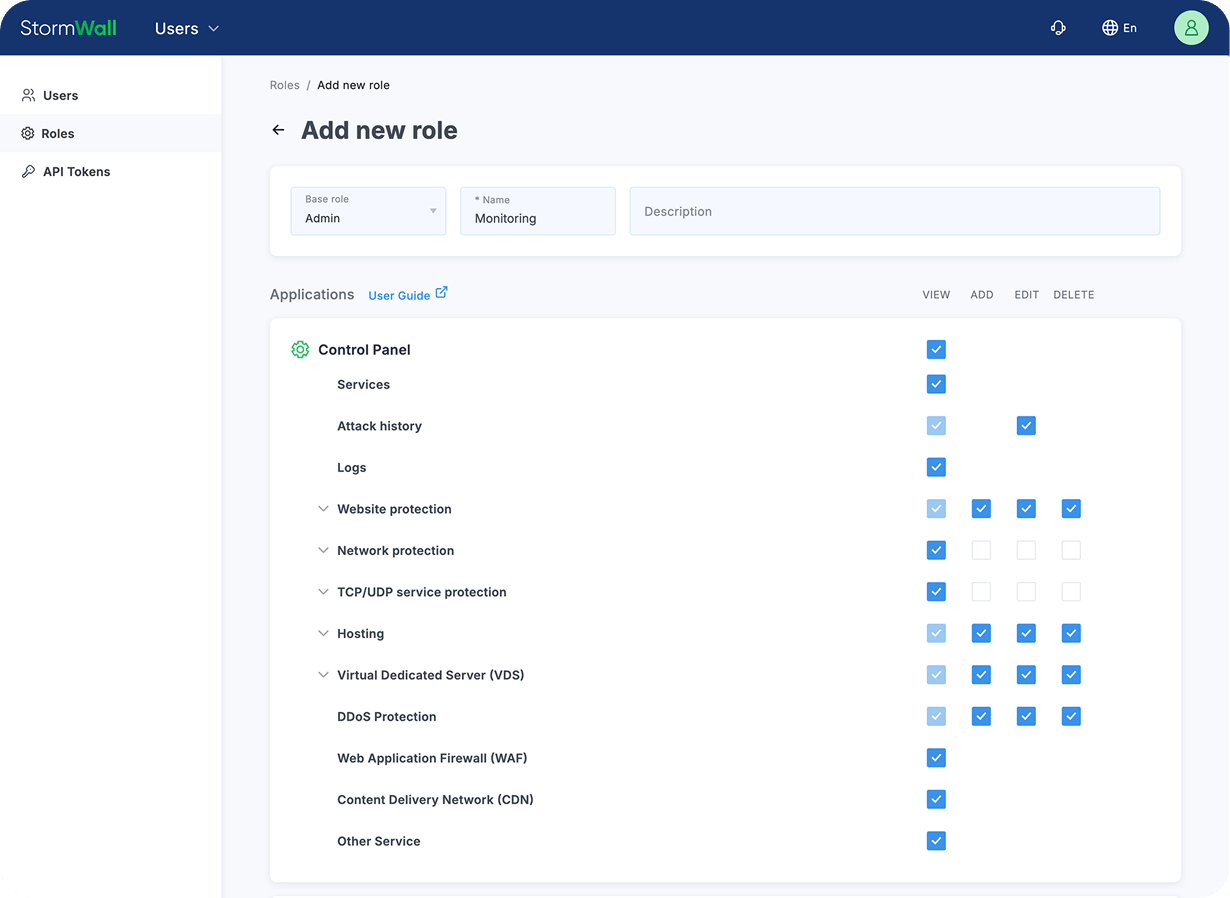
Sub-accounts and roles — Client Portal
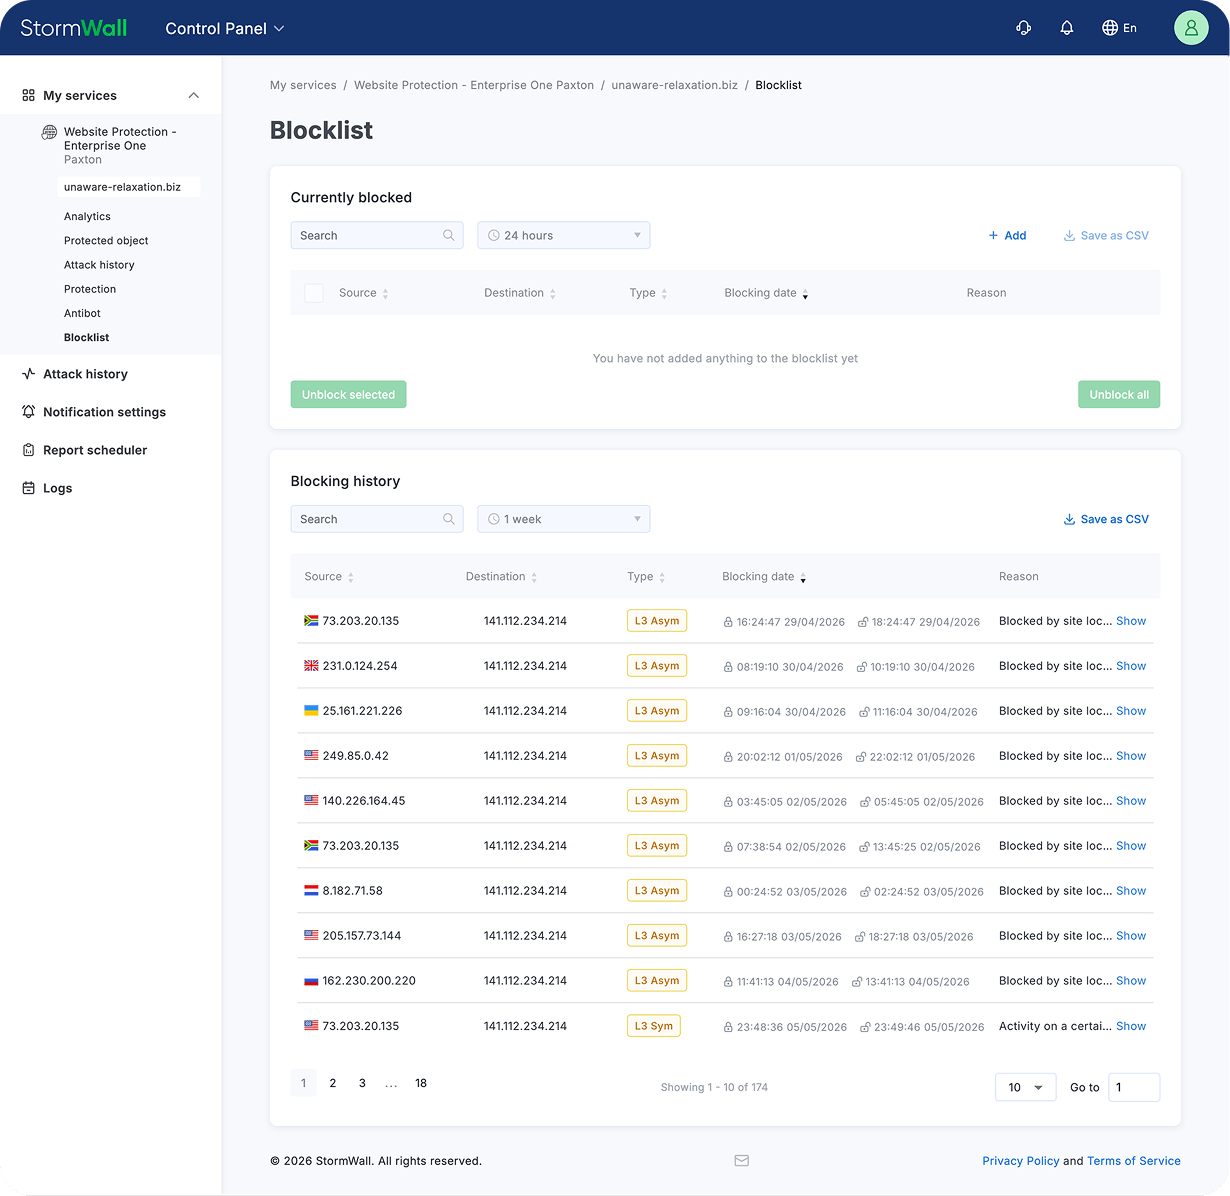
Block lists — Client Portal
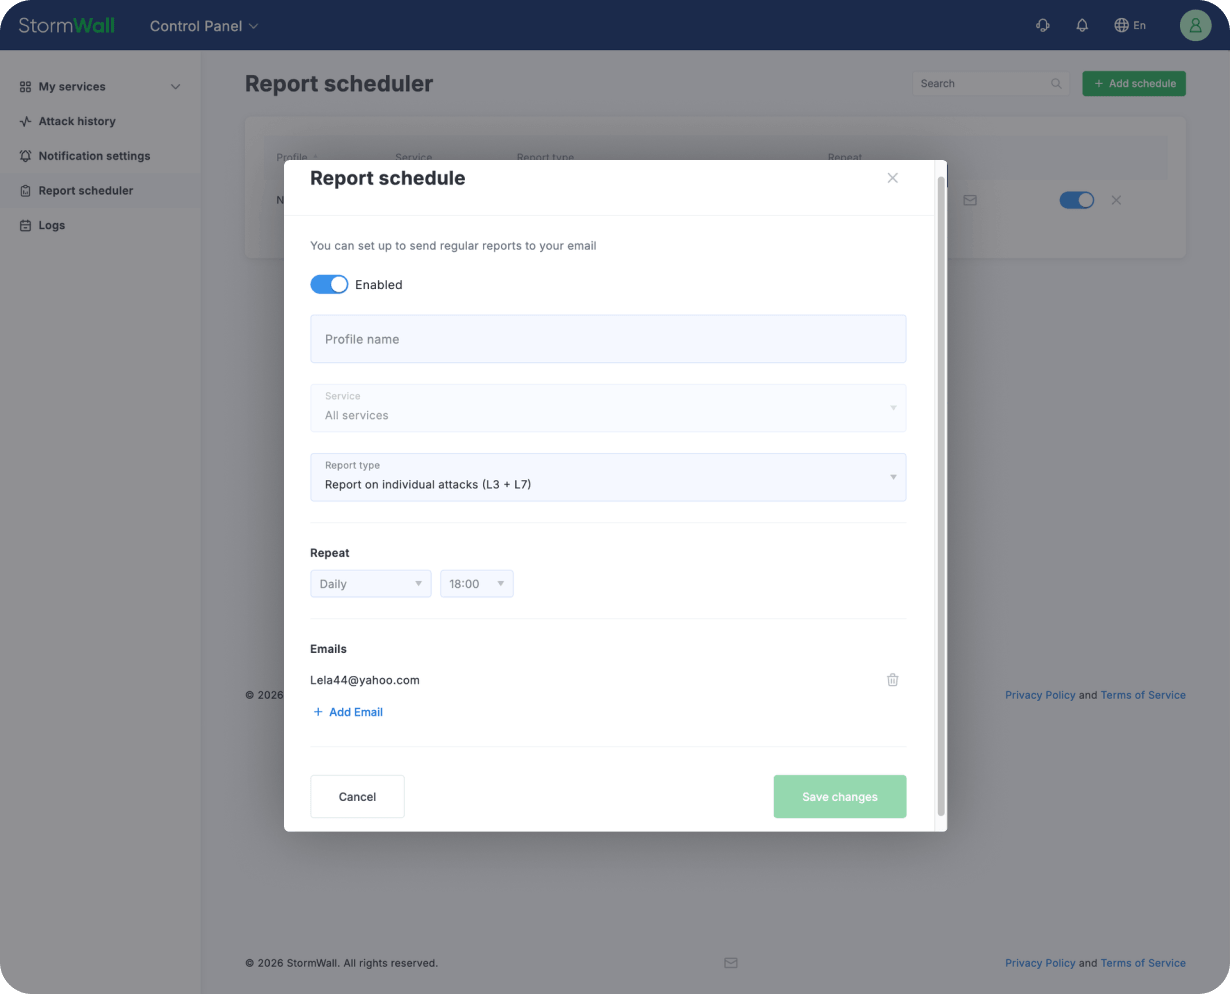
Report scheduler — Client Portal

StormWall Global
Scrubbing Network

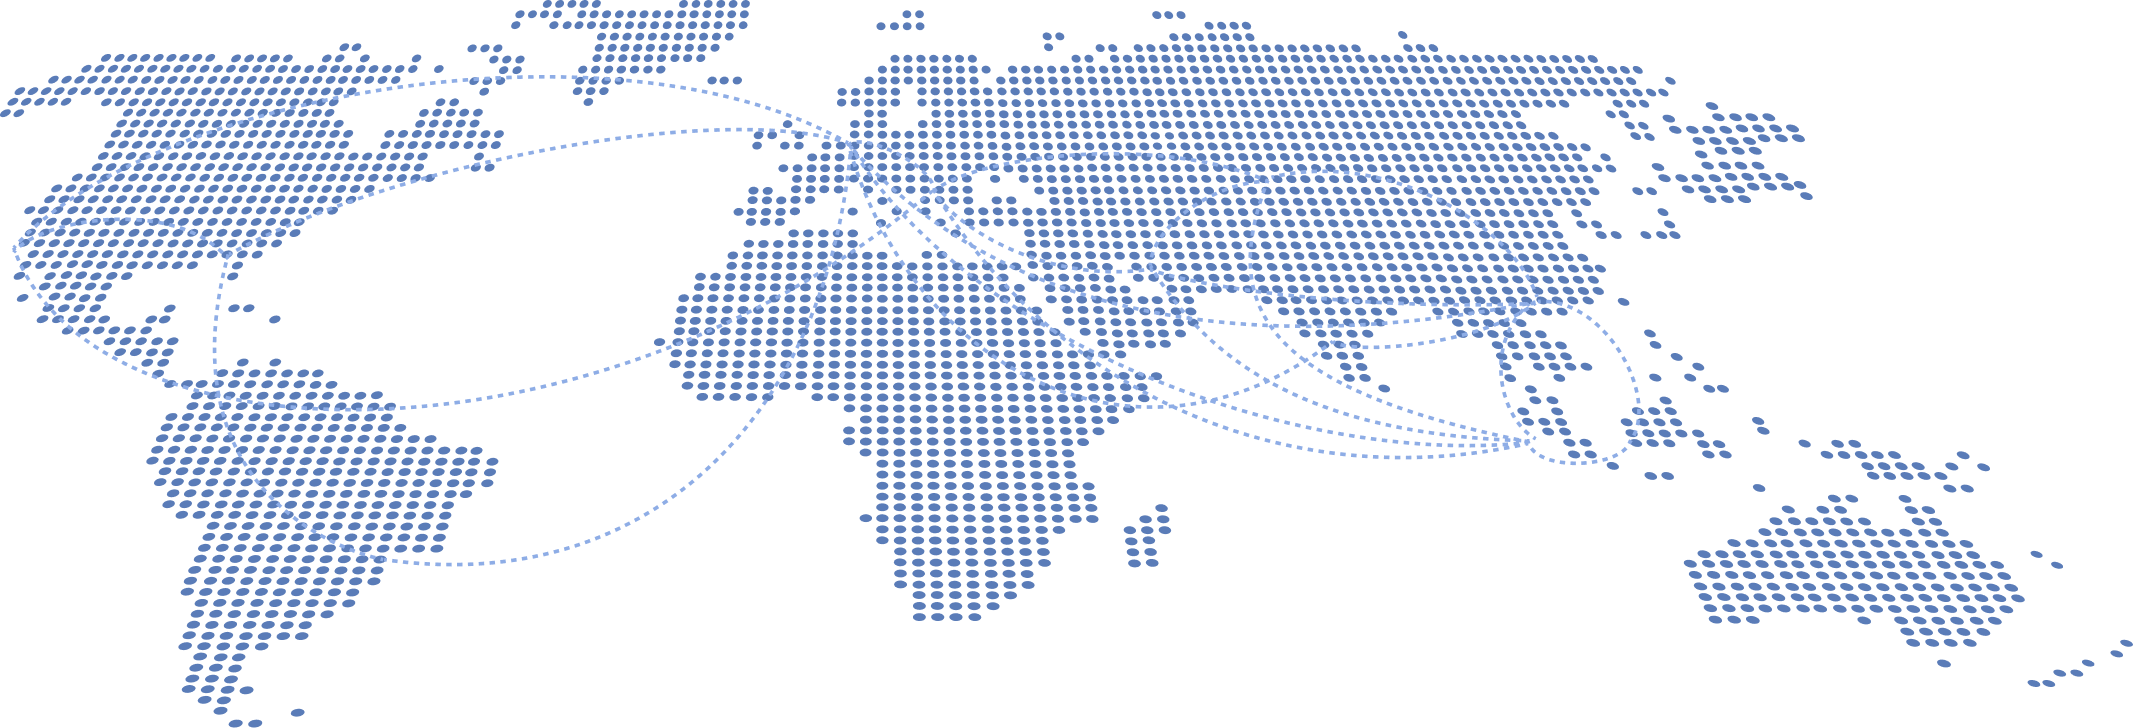
9 filtering points on 3 continents, connected by anycast and 25+ Tier-1/Tier-2 uplinks.
Your traffic reaches the nearest PoP. Attacks are dropped there. Clean packets travel on.

  • Miami
  • Los Angeles
  • Frankfurt x2
  • Hong Kong
  • Singapore
  • Dubai
  • Sofia
  • Jakarta
  • São Paulo Coming in 2026
  • Mumbai Coming in 2026
  • Almaty Coming in 2026

8+ Tbps

Total
capacity

3+ Tbps

Largest attack
mitigated

9

Global
PoPs

StormWall vs Competition

Capability StormWall Protection as a core Competition CDN-first
False-positive rate 0-0.1% ~2-5% (industry avg, not disclosed)
Managed by a team SOC engineers tune your rules Self-service, DIY WAF & Antibot rules
Best quality of support Every plan On high tiers only
Full WAF customization All tiers On high tiers only
Bot Management (JA3/JA4, proxy detection) Included Usually as a paid add-on
Pricing model Clean traffic, no attack-volume bill Opaque quotes
SSL-transparent filtering (PCI DSS) No key exposure Requires key upload or cert mgmt
Time to deploy (under attack) 10 minutes Hours
Core focus DDoS + WAF + Antibot (one bundle) Lots of products, diluted focus
Free trial Full-featured trial Free tier without WAF/Antibot

8 Tbps stops any attack. Scale beyond necessity is marketing, not protection.

Serhat Esmer

Serhat Esmer

Sr. Network Engineer

Rokogame Studios, MMORPG Dev

When it came to Layer 7 protection, StormWall provided the best protection at the lowest cost. Even providers whose licenses cost thousands of dollars couldn't deliver the same results.

Rock-solid protection
from the start

Reason #1

Specialist, not generalist

DDoS protection is our core business for 13 years. We are after one thing: stopping attacks. WAF and Antibot make it complete.

Reason #2

Managed by humans

Our engineers tune your WAF, write your bot rules, and watch your dashboards. You don't configure security. You run a business.

Reason #3

0-0.1% false positives

Lower than industry average. Real customers reach checkout. Real traffic reaches your origin. Quiet confidence, not loud challenges.

Reason #4

Transparent economics

You pay for clean traffic only. No surprise Enterprise walls, no "contact sales" for critical features. Same protection on every tier.

Reason #5

Deploy in minutes

DNS change? Done. No agents, no SDKs, no code. Go live even in the middle of an attack. SSL-transparent option keeps your keys yours.

Reason #6

15-minute SLA

We are always here to handle everything. The answer takes minutes because the engineer already knows your stack.

Protection that adapts
to any industry

Click and see the attacks you face, the risks on your board's radar,
and exactly which of the three modules neutralizes each one.

Fintech Banking Payments

When transactions stop,
the market knows in minutes.

Tight SLAs, strict auditors. An hour of degraded checkout shows up in the quarterly report. A login-flow credential-stuffing wave shows up in the news.

99.8%

Card testing blocked

Key risks

Transaction API flooding — L7 floods on payment and auth endpoints during peak volume.

Credential stuffing at scale — automated login replay coordinated with carding and money laundering.

Card testing on checkout — stolen cards validated in bulk before dark-market resale.

PCI DSS key exposure — handing SSL keys to your vendor can invalidate compliance.

How we protect

Anti-DDoS · L7 edge

Advanced WAF · API & fraud rules

Antibot · JA3/JA4 fingerprinting

SSL-free filtering · PCI DSS-friendly

PCI DSS SOC 2 ISO 27001 SWIFT CSP
E-commerce Retail

Black Friday doesn't wait
for your WAF tuning.

Retail spikes 10–40× on peak days. Scrapers, card-testers, and coupon bots mix with real customers. Every false-positive block is a lost sale.

99.96%

Real customers preserved

Key risks

Price & inventory scraping — competitor bots pulling data minutes after a launch.

Coupon & loyalty abuse — automated redemption across fake accounts.

Checkout DDoS on peak days — L7 floods timed to Black Friday / Prime Day.

False positives killing revenue — a 2–5% WAF misfire on 10M sessions = 200k–500k bounced checkouts.

How we protect

Antibot · low-friction challenge

Advanced WAF · card-testing guard

Anti-DDoS · peak-day absorption

Low false-positive rate

PCI DSS GDPR CCPA
Gaming eSports

A 200ms spike
is a refund request.

Latency is the product. Attacks don't have to take you down — just slow you down during ranked matches, tournaments, launches.

< 5 ms

Added latency

Key risks

Volumetric floods on match servers — UDP/NTP/SYN during peak play.

DDoS-for-hire against rivals — booters targeting streamers and tournament players.

Item-duping & economy bots — draining in-game marketplaces in hours.

Launch-day traffic storms — legit + attack traffic indistinguishable.

How we protect

Anti-DDoS · UDP/TCP filtering

GRE tunnel · low-latency

Antibot · economy-API defense

+0 ms TTFB overhead

TCP/UDP Anycast Low-latency
Media Streaming News

Election night is
the worst time for a ticket.

Media serves the world on the minutes that matter most. That's exactly when scraping, L7 floods, and content theft peak.

+340%

Peak traffic served

Key risks

Breaking-news traffic spikes — 10–100× regular load within minutes.

Content scraping & republishing — paywalled content pulled at scale.

State-level censorship attacks — politically-timed DDoS on reporting windows.

Paywall bypass automation — headless browsers rotating IPs to dodge limits.

How we protect

Anti-DDoS · spike absorption

Antibot · scraping & paywall

CDN-ready integration

Multi-PoP failover

GDPR Press-freedom
SaaS API platforms

Your SLA is
everyone else's SLA.

When you're a platform, one attack cascades into outages across hundreds of customer apps. Uptime is contractual with teeth.

99.996%

Uptime delivered

Key risks

API flooding & abuse — rate-limit evasion at scale across rotating sources.

Tenant-to-tenant propagation — a compromised tenant attacking the platform.

Credential stuffing on SSO — leaked passwords replayed at scale.

Zero-day exploit spray — a new CVE swept across every exposed instance.

How we protect

Advanced WAF · virtual patching

Antibot · API behavioral rules

Anti-DDoS · L7 API defense

API-first management

SOC 2 Type II ISO 27001 GDPR
Government Public sector

The threat model starts
with nation-states.

Public infrastructure attracts the most sophisticated attackers on earth. Legal and regulatory constraints require regional data residency.

Quarterly

Red-team exercises

Key risks

Politically-timed DDoS campaigns — synced with elections and announcements.

Citizen-portal defacement — SQLi/XSS for data access or public embarrassment.

Data-residency non-compliance — foreign CDNs may violate regulations.

Critical-infrastructure SLAs — minutes of downtime turn into hearings.

How we protect

Anti-DDoS · dedicated capacity

Advanced WAF · OWASP & virtual patching

Regional data residency

Dedicated installation available

ISO 27001 SOC 2 GDPR
Telecom ISP Datacenter

You're the backbone.
Attackers know it too.

An ISP absorbs attacks meant for every customer on its network. One bad afternoon = angry tenants and SLA refunds.

3+ Tbps

Largest mitigated

Key risks

Customer-directed volumetric floods — multi-Tbps saturating your uplinks.

Booter marketplace activity — rented devices on your network attacking elsewhere.

Upstream transit congestion — attacks spilling onto peering links.

BGP-level prefix attacks — entire ASN ranges targeted.

How we protect

BGP protection · ASN/IP pools

GRE / L2VPN transport

Symmetric + async filtering

Deploy during active attack

Anycast BGP GRE/IPIP
Crypto Exchanges Wallets

Downtime isn't loss.
Downtime is exit liquidity.

Downtime during volatility means users switch to competitors permanently. Plus drainer bots, sniping, and 2FA-bypass attempts.

100%

Uptime during volatility

Key risks

Volatility-timed DDoS — attacks synced to major market moves.

Withdrawal sniping bots — racing mempools to drain during approvals.

Listing-time scraping — auto-buy milliseconds after token release.

Account takeover & 2FA bypass — SIM-swap coordinated stuffing.

How we protect

Anti-DDoS · volatility-proof

Antibot · sniping & drainers

Advanced WAF · API & 2FA guard

15-min SLA · 24/7

SOC 2 ISO 27001 24/7 SOC

How an attack unfolds
in real time

Under attack, here's the actual minute-by-minute of what our SOC
does while you're reading the alert.

T+0s

T+00:00

Attack hits the edge

980 Gbps SYN flood aimed at your A-record. 2.8M rps shortly after. Mixed L3/L7.

Detected

3s

T+00:03

Auto-mitigation engages

BanHammer AI classifies the pattern in 3 seconds.
Drop rules push to all 9 PoPs. 92% of the flood dies at edge. No human needed yet.

Sub-second AI response

23s

T+00:23

SOC engineer joins

Our teammate opens the console. He already knows your stack — no onboarding. First diagnostic command typed in 23 seconds flat.

15-min SLA met in 23s

3m

T+03:00

3 Tbps peak absorbed

Combined L3 + L7 + Antibot evasion bursts to 3.1 Tbps. Our global PoPs absorbing the traffic burst. Custom JA4 drop rule deployed by our engineer targets only the toolkit.

Peak. Origin untouched

5m 30s

T+05:30

Attack over. Report ready

Malicious actors give up. TTFB: +0 ms. False positives: 0.04%. Incident report in your Client Portal — timestamped, exportable, auditor-ready.

Audit trail. SOC 2 / PCI ready

That's how we mitigate attacks.

Total customer-facing impact: 0 sec. Ops-team wake-ups: 0. Messages you had to send: 0. This is what our "managed protection" means.

Network-level protection
(L3-L5 anti-DDoS)

We stop volumetric and protocol attacks before they reach your infrastructure, letting only legitimate TCP/UDP traffic through.

L3-L5 DDoS SYN, TCP, UDP

Malicious Bots Scraping, Brute-Force, Credential Stuffing, etc.

Hacker Attacks SQLi, XSS, OWASP Top 10, etc.

Legitimate TCP/UDP + HTTP(S)

L3-L5 Filter

L7 DDoS HTTP(S) Flood

Malicious Bots

Hacker Attacks

Legitimate TCP/UDP + HTTP(S)

WAF

Anti-DDoS

Antibot

Clean & Secure Traffic

Stable & Protected Web Resources

Alfian Pamungkas Sakawiguna

Alfian Pamungkas Sakawiguna

SEO

IDCloudHost, Cloud Service Provider

Over three years, not a single minute of downtime due to DDoS — even during peak attack periods. It's not just a "shield" — it's the foundation that lets our clients run their businesses without constantly looking over their shoulder.

Pick an attack.
See how we block it.

Click a threat type — see which of the three modules intercepts
it and where exactly in the stack.

Choose an attack vector

See the result

Volumetric DDoS

DDoS Protection SYN/UDP flood dropped at scrubbing PoP
Filtered
WAF Not needed — attack never reaches L7
Not triggered
Antibot Not needed — dropped upstream
Not triggered

Mitigated in ~3s — our edge scrubbing engine matched the SYN-flood pattern. Your origin never saw a packet.

See the result

L7 HTTP Flood

DDoS Protection High-rate request spike detected
Filtered
WAF Behavioral model flagged abnormal patterns
Blocked
Antibot JA3/JA4 fingerprints identified the attack toolkit
Identified

Multi-layer catch — DDoS thinned the flood, the WAF inspected the survivors, Antibot fingerprinted the toolkit. Real users never queued.

See the result

SQL Injection

DDoS Protection Not applicable — valid single request
Not triggered
WAF Advanced WAF · OWASP A03 match · payload dropped
Blocked
Antibot Not needed — blocked at the Advanced WAF
Not triggered

Payload dropped — a managed rule matched the injection pattern. Virtual patching keeps you covered hours after disclosure, not weeks.

See the result

Stored XSS Attempt

DDoS Protection Not applicable
Not triggered
WAF Advanced WAF · XSS payload sanitized
Sanitized
Antibot Not needed
Not triggered

Sanitized at the Advanced WAF — the stored-XSS payload was caught in the POST body. Our SOC tunes the rules to your form schema.

See the result

Credential Stuffing

DDoS Protection Traffic within baseline
Not triggered
WAF Advanced WAF · login endpoint rate-limited
Rate-limited
Antibot JA3/JA4 fingerprint matched a known bot toolkit
Blocked

Account takeover prevented — fingerprinting and behavioral scoring killed the replay. Real users log in as usual, with no added friction.

See the result

Scraping & Price Bots

DDoS Protection Traffic within baseline
Not triggered
WAF Requests are technically valid
Not triggered
Antibot Bot fingerprint + behavioral scoring → drop
Blocked

Scraping neutralized — Antibot separates automated clients from real browsers. Googlebot still passes. Your pricing stays yours.

See the result

Slow POST / Slowloris

DDoS Protection Keep-alive exhaustion detected · connections reset
Blocked
WAF Not needed — attack killed at L7 DDoS
Not triggered
Antibot Not needed
Not triggered

Connections reset — L7 heuristics caught the stalled sockets. Your worker pool stays free for paying customers.

See the result

RCE / SSRF Attempt

DDoS Protection Not applicable
Not triggered
WAF Advanced WAF · OWASP A10 match · payload dropped
Blocked
Antibot Not needed
Not triggered

Dropped at the Advanced WAF — command-injection and SSRF vectors blocked. Your internal services stay internal.

Honest answers.
Your doubts dispelled

What is website DDoS protection?

StormWall for Web analyzes and filters all incoming traffic across OSI layers L3–L7. Malicious or “junk” requests are blocked, while only legitimate traffic reaches your website or web application.

Connection is performed via proxying, with no need to change your hosting provider. If you use your own networks (BGP), protection can be configured without changing your IP address. After activation, your website is protected from DDoS attacks and malicious traffic targeting both network and application layers.

What types of L3–L7 DDoS attacks does StormWall block?

StormWall protects websites and web applications from both network-layer and application-layer DDoS attacks. At the network level, the service mitigates attacks such as SYN Flood, UDP Flood, ICMP Flood, TCP Reflection, and amplification attacks including NTP, DNS, and SSDP. At the application layer, StormWall blocks HTTP Flood attacks (GET/POST), Slowloris, and other sophisticated attacks, including bot-driven traffic.

Who is website DDoS protection suitable for?

StormWall for Web is suitable for any organization that operates a website or web application, including retail and e-commerce companies, government organizations, media platforms, financial institutions, insurance providers, and more. The solution scales to any traffic volume and adapts traffic filtering to the specific characteristics and needs of each business.

How is StormWall website protection different from standard ISP DDoS protection?

Unlike basic provider-level protection, StormWall uses dedicated filtering centers, intelligent traffic analysis, and machine learning technologies. Our engineers develop tailored protection scenarios for each client. In addition, we offer a full set of solutions for comprehensive web application protection, including Antibot, WAF, and CDN, ensuring security across all layers from L3 to L7. Protection can be configured both with and without SSL certificate disclosure, while maintaining PCI DSS requirements and keeping confidential data secure.

How quickly can website DDoS protection be activated?

We recommend enabling protection in advance, as the cost of recovering from a serious incident is always higher than the cost of prevention. StormWall for Web DDoS protection can be connected in as little as 10 minutes, allowing fast deployment and immediate protection of web resources from DDoS attacks.

Start a free trial. Today.

Full WAF + Anti-DDoS + Antibot stack. 10-minute deployment.
No credit card required. No lock-in. And no sales pressure.

  • Live protection within 10 minutes of sign-off
  • Full access to the feature set
  • Migration assistance for existing setups
  • Keep us or cancel — no migration fees either way

Tell us about your project

First Name
Last Name
Company
Phone
Email
Comment (optional)

Compare plans

Features Personal Business Enterprise
Level 2 domains 1 1–4 and up to 100 1–4 and up to 100
Subdomains per domain 10 100 100
Bandwidth 25 Mbit/s 50–10 000 Mbit/s 50–10 000 Mbit/s
Support response time (24/7) up to 3h up to 30 min up to 15 min
Uptime SLA 98% 99.2% 99.5%
Proactive monitoring Not included Not included Included
Chat support Not included Not included Included
Dashboard Included Included Included
Attack-source heatmap Included Included Included
Top countries & traffic Included Included Included
Block history Included Included Included
Rule editor Included Included Included
DNS record management Included Included Included
Report export Included Included Included
Scheduled reporting Included Included Included
Service management API Included Included Included
Customizable error pages Add-on Add-on Included
Extended logging 2 days 2 or more days 2 or more days
Notifications (chat / email / webhook) Included Included Included
RBAC (Role‑Based Access Control) + audit log Included Included Included
Graylog log access Not included Not included Included
L3–L7 filtering: 8 000+ Gbps (unmetered) Included Included Included
Free SSL Included Included Included
HTTPS/HTTP2 Included Included Included
WebSocket (80/443) Included Included Included
Always-on + on-demand modes Included Included Included
Caching (HyperCache) Included Included Included
Protected DNS Included Included Included
Load balancing across back-ends Not included Included Included
WebSocket on custom ports Not included 4 (more on request) 4 (more on request)
L7 filtering without SSL disclosure (log-over-UDP) Not included Not included Included
BGP connectivity Not included Not included Included
Connectivity on site Not included Not included Included
Dedicated IP Not included Not included Included
GeoIP / geo-blocking Included Included Included
Header / path filtering Included Included Included
White / black lists (per service) 100 1 000 (up to 10 000) 5 000 (up to 10 000)
Grey lists Not included 1 000 1 000
Cookie checks Included Included Included
JavaScript challenge Included Included Included
HTTP redirect Included Included Included
CAPTCHA Included Included Included
JA3 / JA4 fingerprinting Not included Not included Included
HTTP rule chains Not included Not included Included
Positive / negative models Not included Not included Included
Pass / limit / challenge / block rules Not included Not included Included
ML detections Not included Not included Included
OWASP Top 10 Not included Included Included
HTTP protocol validation Not included Included Included
Automatic static-content filtering Not included Included Included
Application-wide rate limiting Not included Included Included
Anomaly-based blocking (LRU) Not included Included Included
False-positive suppression (ML + analysts) Not included Included Included
Business-logic WAF (application model, ML) Not included Not included Included
User & session control Not included Not included Included
Session-level authorization control Not included Not included Included
Per-action rate limiting Not included Not included Included
API validation (OpenAPI) Not included Not included Included
SIEM integration Not included Not included Included
Warm-data storage + retrospective analysis Not included Not included Included
WAF API + portal write access Not included Not included Included
Raw queries / parse trees Not included Not included Included
Dedicated installation Not included Not included Included