
 +44 20 3695 6722
 Sign in
Legitimate
TCP/UDP Traffic

DDoS Protection for TCP/UDP Services

StormWall for Servers
Stable operation of TCP/UDP services with minimal costs
and maximum connection flexibility

Reliable Protection
Block all DDoS attacks on
TCP/UDP

Unlimited Traffic
No restrictions, handle any load

Full Port Security
Secure any number of ports effortlessly

Multi-Layer Defense
L3-L5 filtering for maximum stability
Who Needs
TCP/UDP DDoS Protection
StormWall for Servers is designed for a wide range of clients: from gaming servers and
business applications to telecom operators, including ISPs, hosting providers, and data
centers.

Gaming Services
Main risks:
- Unplanned downtime resulting in losses
- Delays that ruin the gaming experience
- Player loss due to frequent outages

Business Applications
Main risks:
- Disruption of essential functions
- Direct financial impact
- User churn

Providers & Data Centers
Main risks:
- Service quality and SLA degradation
- Customer migration to competitors
- Client data breaches
Why Choose StormWall
for Server DDoS Protection
Our DDoS protection solution for TCP/UDP offers reliable filtering of all types of
malicious traffic, ensuring uninterrupted operation of your resources. We guarantee
flexibility, scalability, and high-efficiency protection tailored to your needs.
And all of this comes with no additional costs—just a subscription to our service!
What You Get

Guaranteed 24/7 availability of your services

TCP/UDP protection on L3-L5 OSI layers for comprehensive security

Flexible connectivity with tunneling or proxying

No limits for incoming traffic volume

Connect any number of ports

Support for various OS and specialized routers

Clients are paying for clean traffic only

24/7 customer support with
a 15‑min response time

Free and fast deployment if
a client is under attack

Security as a Managed service for seamless protection and support
StormWall
Global Scrubbing Network
Our distributed network enables us to mitigate
DDoS attacks closer to their source
> 10 Tbps
Filtering Capacity

- Miami
- Los Angeles
- Frankfurt x2
- Hong Kong
- Singapore
- Dubai
- Sofia
- Jakarta
- São Paulo


Connection Options
01
Tunneling (IPIP/GRE)
Ideal for Unix-based servers (Linux, FreeBSD) or specialized routers (Cisco, MikroTik, etc.). We create a secure tunnel and provide you with an additional Storm IP through which clients interact with your services. This ensures reliable protection while maintaining visibility of all users' original IP addresses.
02
Proxying
Optimal solution for Windows-based servers. All incoming traffic is redirected through the StormWall proxy server, providing a single protected IP address. This connection method requires no complex setup and ensures stable DDoS protection for your services.

Internet


Malicious Traffic

StormWall Cloud
IPIP/GRE Tunnel or Proxy

Client's Server
with StormWall IP
with StormWall IP
How We Filter Traffic
All of your server’s inbound traffic is cleaned up in three stages:
- Edge Routers
- Hardware Filters
- Stateful Filters
Edge Routers
Over 100 of our border routers worldwide are configured to block malicious traffic, ensuring robust
protection for your network.
This level of filtering ensures our clients are protected against attacks reaching several hundred gigabits
per second, as it effectively blocks all TCP/UDP amplification.
Hardware Filters
The majority of TCP/UDP flood traffic is blocked, ensuring high packet processing speeds.
The load is evenly distributed across multiple hardware filters.
Stateful Filters
At this level, we block even the most sophisticated threats, including those involving bots.
Full Control Over
TCP/UDP DDoS Protection
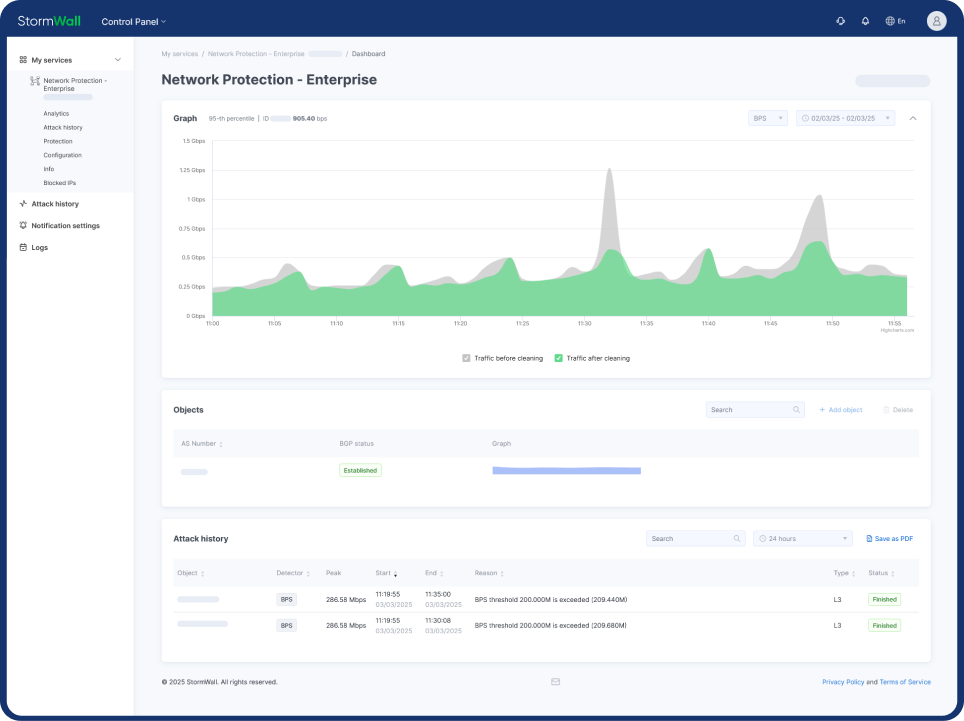
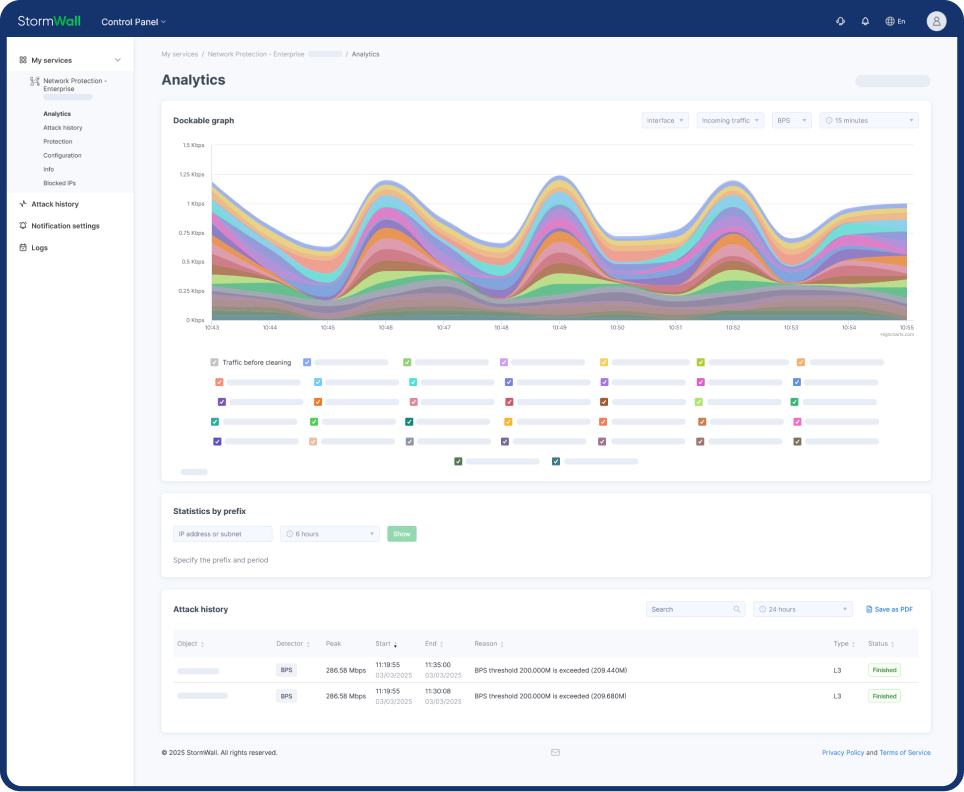
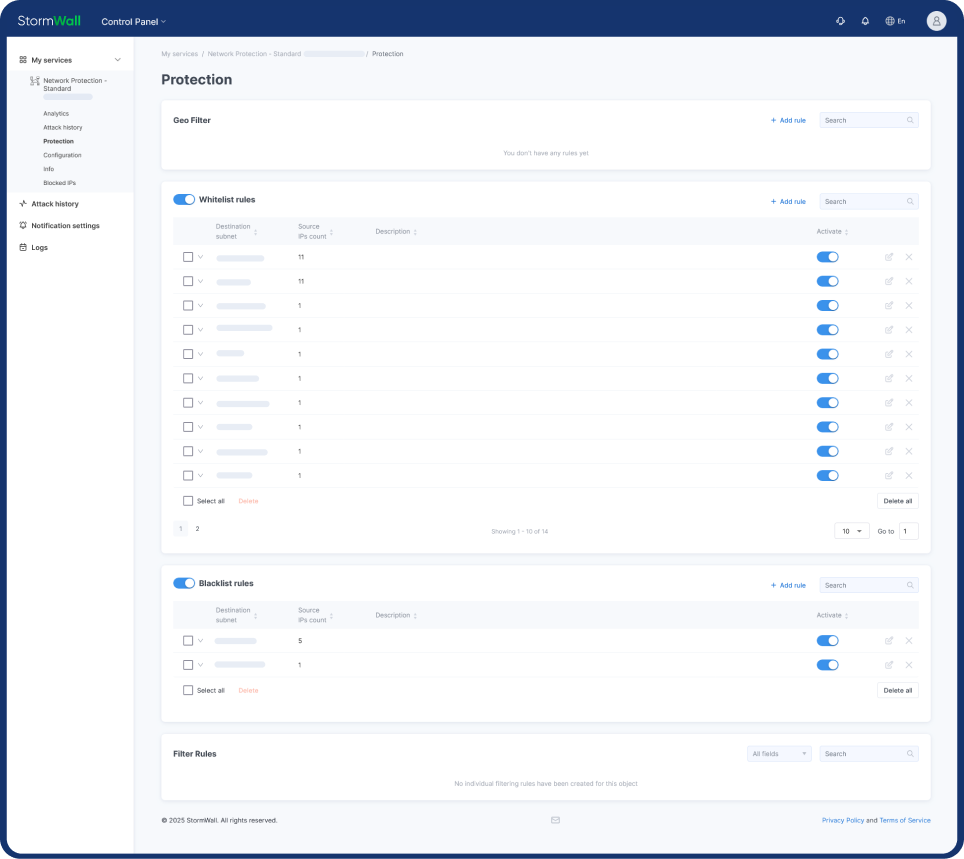
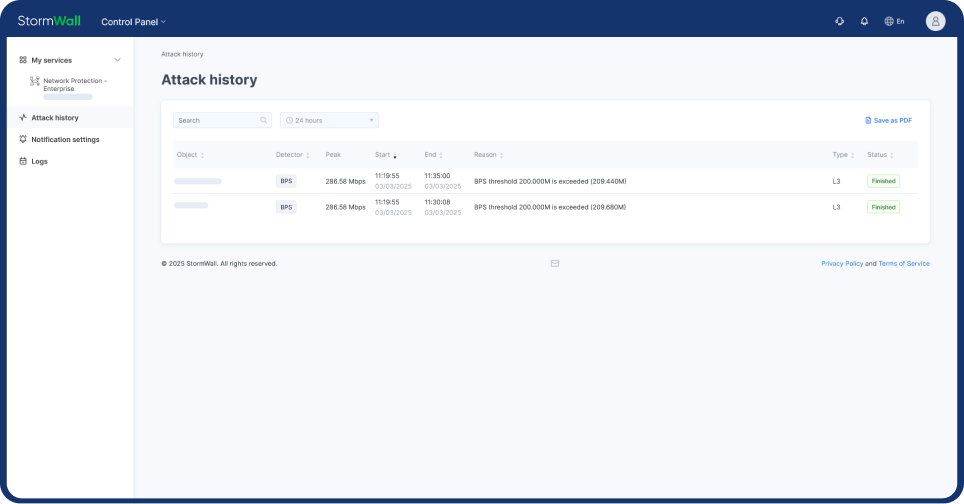
The StormWall Client Portal offers complete control over protection settings. It's modern, functional, and user-friendly, allowing for quick mastery in just a few minutes.
- Real-time analytics
- Customizable filtering rules
- Attack history for future reference
- Requests, traffic data, and response codes analytics
- Automated attack notifications
- Detailed PDF reports
- Sub-accounts and role management
StormWall for Servers
Pricing Plans
Payment period

Compare plans
Currency:
 USD
 EUR
 USD
EUR
USD
EUR
USD
EUR
Standard
Bandwidth


50 Mbit/s

Additional options

Additional rented
IP address
0
Tunnels
1
Custom protection profiles

Response time for request
up to 60 min
Attack protection capacity
up to 600 Gbps
Guaranteed availability
99,2 %
Chat support
Business
Bandwidth
50 Mbit/s
Additional options
Additional rented
IP address
0
Tunnels
1
Custom protection profiles

Response time for request
up to 30 min
Attack protection capacity
unlimited
Guaranteed availability
99,5 %
Chat support
Enterprise
Bandwidth
600 Mbit/s
Additional options
Additional rented
IP address
0
Tunnels
1
Custom protection profiles
Response time for request
up to 15 min
Attack protection capacity
unlimited
Guaranteed availability
99,9 %
Chat support
Frequently Asked Questions
What is TCP/UDP service DDoS protection?
StormWall for Servers analyzes and filters all incoming traffic across OSI layers L3–L5. Malicious traffic is blocked before it reaches your infrastructure, while only legitimate user traffic is delivered to your services. The solution can be connected via IPIP/GRE tunnel, proxying, or direct integration at the hosting site. After activation, your TCP/UDP-based services are protected from DDoS attacks and remain continuously available.
What types of L3–L5 DDoS attacks does StormWall block?
StormWall protects TCP/UDP services from network and protocol-based attacks, including UDP Flood, SYN Flood, ACK Flood, TCP Flood, and other common types of DDoS threats targeting service infrastructure.
Who is TCP/UDP service protection suitable for?
StormWall for Servers is suitable for organizations that need to protect specific services within physical or cloud infrastructure. This includes online gaming platforms, IP telephony, mail services, IPTV, VPN services, and other TCP/UDP-based applications. No autonomous system (AS) is required — a public IP address is enough.
How is StormWall TCP/UDP protection different from standard ISP protection?
Unlike basic provider-level protection, StormWall uses dedicated filtering centers, intelligent traffic analysis, and machine learning technologies. Our engineers develop tailored protection scenarios for each client. The solution scales according to attack volume, supports protection for custom ports and specialized TCP/UDP protocols, and operates without impacting legitimate users.
How quickly can StormWall TCP/UDP protection be activated?
We recommend enabling protection in advance, as the cost of recovering from a serious incident is always higher than the cost of prevention. StormWall protection for TCP/UDP services can be connected in as little as 15 minutes
